Security

AI agents your security team can sign off on

Every agent action has permissions, a record and a way back. If a control isn't ready yet, we say so.

Inside the product

Controls, built into the product

Release controls, readiness checks and clear error explanations live where the work happens, not in a separate audit tool.

  • Regression suite412 tests · run 2h agoPassing
  • Data migration dry run0 errors on copy of production dataPassing
  • Accessibility review2 findings open since last weekNeeds review
  • Performance baselineNever run against this buildUnknown

Approvals

  • QAQA leadFindings accepted, non-blocking.Approved
  • AHRelease ownerPending

QA sign-off

Waiting on 1 approval. Record the QA sign-off to proceed.

Interactive UX concept; sign-offs and other actions affect only the preview.

Platform settings — infrastructure automation coverage
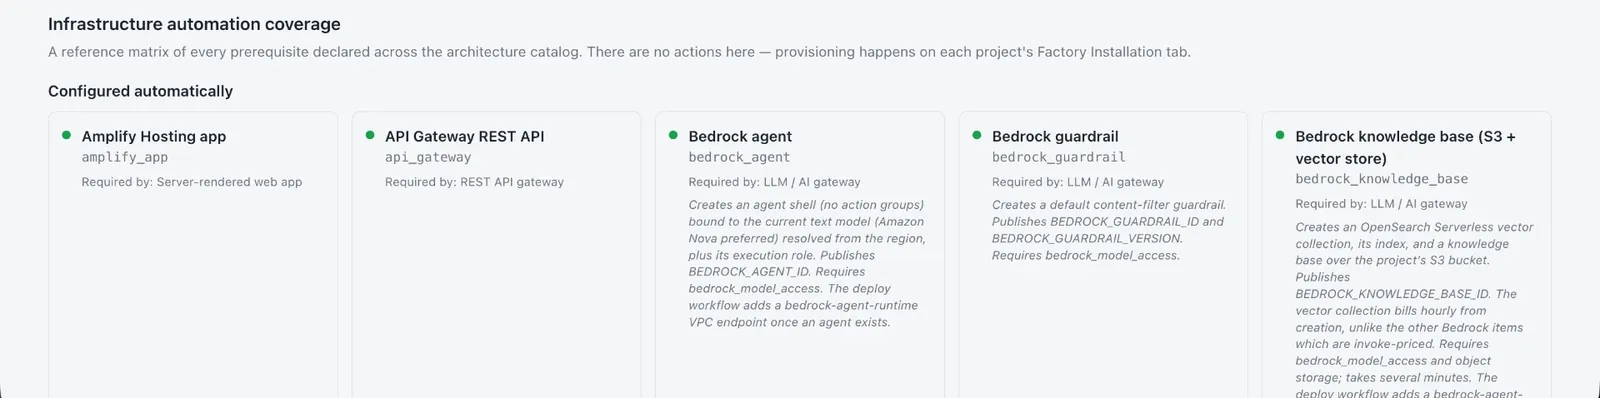
ASE platform settings screen showing cloud account configuration and the share of infrastructure covered by automation.
ASE product screenshot — captured September 2026

Cloud accounts, roles, policies and hosted zones are configured once, then reused by every workspace. Account identifiers are masked in this capture.

One set of rules for every workflow

Permissions, approvals and records apply the same way everywhere.

Enterprise control plane

Policies enforced

Agents and people work under explicit roles: approvals gate the lifecycle, every artifact is traceable, security checks run before release and every release stays reversible.

  • Role-Based Permissions & Bounded Authority

  • Named Human Approval & Control Gates

  • End-to-End Requirement-to-Code Traceability

  • Architecture & Design Policy Enforcement

  • Isolated & Controlled Agent Execution

  • Continuous Automated Security Validation

  • Evidence-Backed Release Governance

  • Agent Performance & Quality Monitoring

  • End-to-End Change & Decision Lineage

  • Human-Accountable Exception & Escalation Handling

  • Tested Rollback & Reversibility Controls

How each control works today

Open any control to see what's in place now.

Access & isolation

3 controls

Safe releases

3 controls

Data & models

2 controls

Approvals & records

3 controls

Compliance

1 control

See the controls in an example project

See where approvals, records and rollback apply in a full project.

ExampleProcessManufacturing

Enterprise Process Transformation

Procure-to-Pay Control Tower

A global manufacturer runs procurement through email, spreadsheets and different ERP workflows across twelve business units.

  • Policy-driven intake
  • Three-way match visibility
  • Exception workflows
  • Audit-ready lineage

DISCOVER · DEFINE · BUILD · OPERATE

ExampleModernizationFinancial Services

Legacy Modernization

COBOL Core Modernization

A financial-services company depends on a 30-year-old mainframe application for account servicing and fee calculation.

  • Behavior discovery
  • Business-rule recovery
  • Incremental extraction
  • Equivalence evidence

DISCOVER · DEFINE · VALIDATE · DEPLOY

What we promise

  • People approve at key points
  • Every agent output can be inspected
  • Agents never act outside their permissions
  • We state limits instead of implying features

We only claim what's already in place. Certifications and audits stay marked as coming soon until they're done. We're happy to walk your security team through every control.